Outback Steakhouse Closures and Data Privacy Risks
Outback Steakhouse's recent location closures raise concerns about customer data security and what happens to records when restaurants shutter. Industry experts warn of potential breaches during business transitions.
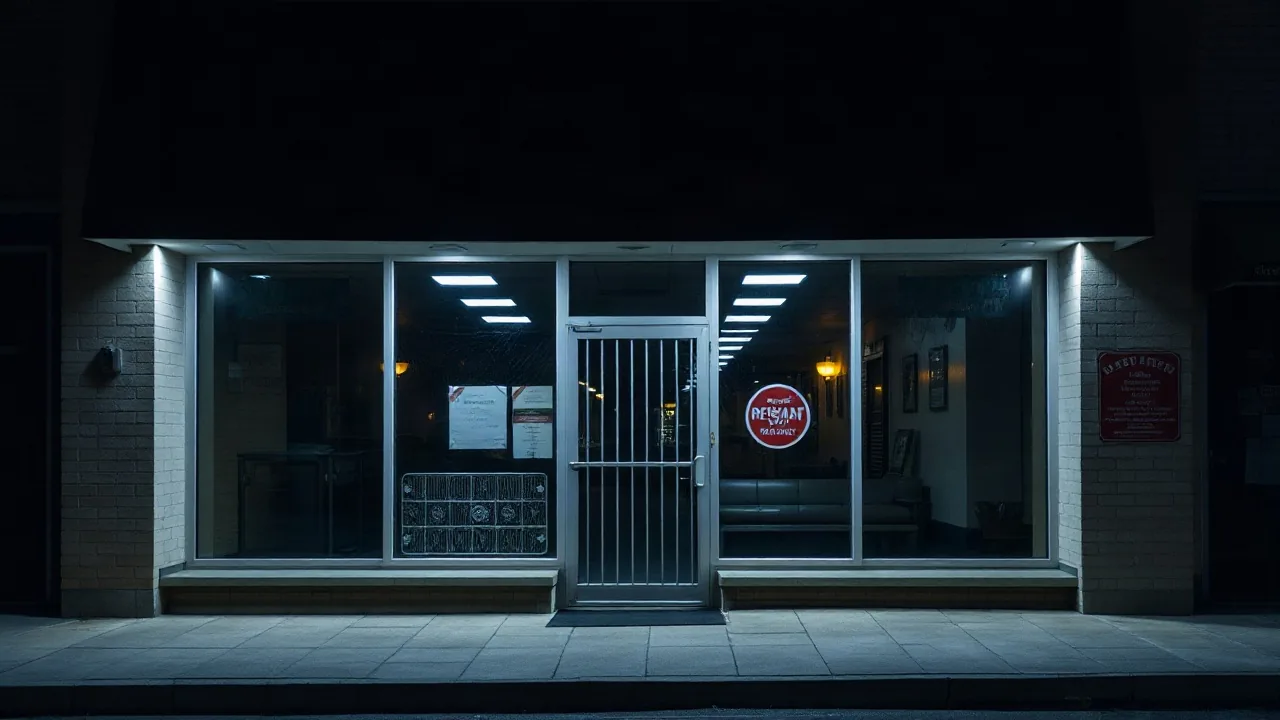
Outback Steakhouse announced the closure of multiple locations across the United States in November 2026, triggering concern among cybersecurity professionals about how the chain will handle sensitive customer information during the shutdown process. The parent company has not disclosed the exact number of closures, but regional reports indicate at least 30 locations are affected, with operations ceasing by year-end.
When restaurants close, they often leave behind databases containing years of customer transaction records, loyalty program data, and payment information. This creates a critical window of vulnerability where data privacy protections may weaken as operational oversight diminishes and IT staff are reassigned or furloughed.
"Restaurant closures are a significant risk vector that often gets overlooked in security planning," said Marcus Chen, principal analyst at Redline Security Advisors. "We frequently see companies fail to properly decommission systems or migrate customer data securely during store shutdowns, leaving information in limbo on unsecured servers."
What Happens to Customer Records
Outback operates a loyalty program called the Bloomin' Rewards, which collects customer email addresses, phone numbers, and spending history. Closed locations typically archive this data rather than delete it, but the transition process is often chaotic.
The chain has not yet published a formal data handling protocol for the affected closures. Industry standard practice requires:
- Secure migration of customer databases to centralized systems
- Encryption of data in transit and at rest
- Decommissioning of on-premise servers with certified data destruction
- Notification to affected customers if any breach occurs during transition
- Audit trails documenting access to customer records
Outback Steakhouse did not respond to requests for comment on their data protection measures during the closure process. The company's parent, Bloomin' Brands Inc., manages approximately 1,000 restaurants across multiple chains, making this a substantial operational and security undertaking.
Previous restaurant industry closures have resulted in exposed customer data. In 2023, a regional casual dining chain left unencrypted payment databases accessible during its shutdown, affecting over 200,000 customers. The incident was discovered by a security researcher months after the restaurant ceased operations.
Broader Business Security and Local Impact
The closures reflect broader challenges in the restaurant sector. Rising labor costs, supply chain disruptions, and shifting consumer behavior have strained traditional casual dining operators. As businesses contract, they often deprioritize business security investments in favor of immediate cost cutting.
Local communities affected by the closures also face indirect security concerns. Closed commercial properties become targets for break-ins and unauthorized access. Criminal actors sometimes use abandoned retail locations to stage data theft operations or establish server farms for malware distribution.
"We've seen closed storefronts become havens for cybercriminals," noted Lieutenant Jennifer Park, who heads the retail crime task force for the National Association of Security Professionals. "An unsecured back office with older IT equipment and no active monitoring is a gift to threat actors."
Outback's security team has not announced plans to physically secure server rooms or point-of-sale systems at closing locations, raising questions about preventative measures being taken.
Regulatory and Consumer Implications
Several states, including California and New York, require businesses to notify customers within 60 days if their personal information is accessed without authorization. The restaurant industry collectively holds millions of customer records, but enforcement of notification rules during business closures remains inconsistent.
Outback customers should monitor their accounts for suspicious activity over the next 90 days. The company's loyalty program data, combined with payment card information from past transactions, makes affected customers attractive targets for identity theft.
Security experts recommend customers take these steps:
- Request deletion of personal data from Outback's systems while the company still has active customer service
- Monitor credit reports and bank statements for unauthorized charges
- Enable fraud alerts with credit bureaus
- Avoid using the same password for other accounts as the one used on Bloomin' Rewards
The closure also highlights gaps in how the restaurant industry manages security risks during transitions. Unlike healthcare and financial services, which face stricter compliance requirements, casual dining establishments operate with minimal regulatory oversight of their data handling practices.
Bloomin' Brands has stated that all affected employees will receive severance packages and that benefits will continue through December 2026. However, the company has not addressed whether IT and security staff will remain employed through the data migration process.
Cybersecurity analysts expect similar closures to continue as consumer spending patterns shift away from traditional full-service restaurants. Without industry-wide standards for secure closure procedures, vulnerable customer data will remain at risk across the sector.